Get 69% Off on Cloud Hosting : Claim Your Offer Now!


- Products
- Solutions
-
Solutions
-
 Cloud
Hosting
-
VPS
Hosting
-
 GPU
Cloud
-
 Dedicated
Server
-
 Server
Colocation
-
 Backup as a Service
-
 CDN
Network
-
 Window
Cloud Hosting
-
 Linux
Cloud Hosting
-
Managed
Cloud Service
-
 Storage
as a Service
-
VMware
Public Cloud
-
Multi-Cloud
Hosting
-
Cloud
Server Hosting
-
Bare
Metal Server
-
Virtual
Machine
-
 Magento
Hosting
-
 Remote
Backup
-
 DevOps
-
 Kubernetes
-
 Cloud
Storage
-
 NVMe
Hosting
-
 DR
as s Service
-
-
Solutions
- Marketplace
- Pricing
- Resources
- Company
 Remote
Backup
 NVMe
Hosting
 Pricing
Calculator
 Unlock Cost
Optimization
 Overview
 Documentation
 Price
Calculator
 Tools
 FAQs
 Terms
of Service
 Privacy
Policy
 Migration
 Container
 Power
 Utilities
 VMware
Private Cloud
 VMware
on AWS
 VMware
on Azure
 Certifications
 Partners
 Careers
 Support
 Service
Level Agreement
 Contact
Table of Contents
- What is AI-powered SIEM?
- Why traditional SIEM struggles
- AI-powered SIEM trends for 2026
- 1. AI-assisted alert triage
- 2. Behavioural analytics and identity threat detection
- 3. AI-assisted investigation and natural-language querying
- 4. AI-driven detection engineering
- 5. Automated response and SOAR integration
- 6. Cloud-native SIEM and multi-cloud visibility
- 7. Unified security data platforms
- 8. Agentic AI in security operations
- 9. Explainable AI and trust
- 10. AI governance and model security
- AI-powered SIEM architecture
- Key AI techniques in SIEM
- Metrics to measure AI-powered SIEM success
- Implementation challenges
- Best practices for adopting AI-powered SIEM
- Strengthen Security Operations with Cyfuture Cloud
- Future outlook
- Conclusion
Security teams today monitor cloud workloads, SaaS applications, identity systems, remote users, third-party connections and on-premises infrastructure, all at once. Each of these produces logs, and each log can hold the one signal that matters. AI-powered SIEM applies machine learning, behavioural analytics and generative AI to security event data so that analysts spend less time sorting alerts and more time investigating real threats.
A traditional Security Information and Event Management (SIEM) platform collects and correlates security events. It does this well, but the volume and variety of modern telemetry can overwhelm even well-staffed teams. This article examines the AI-powered SIEM trends likely to shape security operations in 2026, the limits of each, and what organisations should consider before adopting them.
What is AI-powered SIEM?
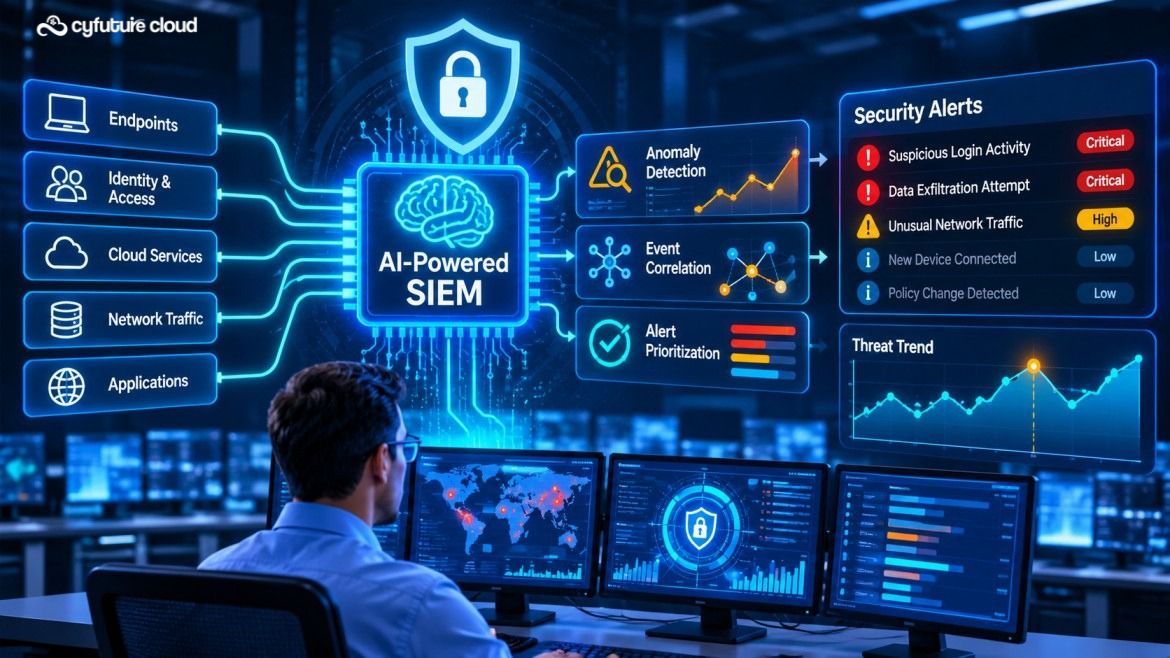
A SIEM platform is a central system that gathers security data and helps teams detect, investigate and report on threats. In practice, a SIEM:
- Collects logs and events from endpoints, servers, firewalls, cloud platforms, identity providers, applications and network devices.
- Normalises that data, meaning it converts different log formats into a common structure.
- Correlates events to detect suspicious patterns.
- Generates alerts for analysts.
- Supports investigation and incident response.
- Retains telemetry for compliance and forensic analysis.
AI-powered SIEM adds several capabilities on top of this foundation:
- Machine learning identifies unusual behaviour and patterns in large datasets.
- User and entity behaviour analytics (UEBA) builds baselines of normal activity for users, devices and services, then flags meaningful deviations.
- Natural-language interfaces let analysts ask questions of their data in plain language.
- Large language models (LLMs) summarise incidents and suggest investigation hypotheses.
- AI agents can assist with triage, enrichment and response recommendations.
- Automation takes over repetitive steps such as lookups and ticket creation.
AI does not remove the need for detection engineering, threat intelligence, incident response expertise or human judgement. It changes where analysts spend their time.
Why traditional SIEM struggles
Conventional SIEM deployments face a consistent set of problems:
- High-volume telemetry from cloud, endpoint, identity and application sources.
- Alert fatigue, where too many low-value alerts bury the important ones.
- False positives that consume analyst time.
- Limited context because data sits in disconnected tools.
- Slow investigations that require manual pivoting between consoles.
- Missed low-and-slow attacks, which spread small actions over weeks to avoid thresholds.
- Skills shortage and burnout in SOC teams.
- Rising ingestion and storage costs.
- Fragmented visibility across hybrid and multi-cloud environments.
A practical example. An administrator logs in from a new country at 2 a.m. A rule-based SIEM may raise a high-severity alert. An AI-assisted system checks more context: Is the device known? Is the user travelling, per the HR or calendar system? Was multi-factor authentication completed normally? Did the session then touch systems the user never accesses? If everything fits a known workflow, the alert can be deprioritised with an explanation. If the login is followed by unusual privilege changes, it rises to the top of the queue.
AI-powered SIEM trends for 2026
The trends below are a mix of established capabilities and emerging ones. Where a capability is still maturing, the article says so. Treat these as informed expectations, not guarantees.
1. AI-assisted alert triage
Triage is the first place most teams see value. AI can:
- Correlate related alerts into a single incident.
- Cluster similar alerts and remove duplicates.
- Score risk using asset criticality, identity sensitivity and business impact.
- Suppress likely false positives based on past analyst decisions.
- Enrich alerts with threat intelligence, asset and user context.
- Summarise an incident in a few readable lines.
The result is a shorter, better-ordered queue. This only works if triage is transparent. Analysts should see why an alert was raised or deprioritised, and be able to override it.
2. Behavioural analytics and identity threat detection
Identity is now a major attack surface, particularly in cloud-heavy environments, because stolen credentials and session tokens let attackers appear as legitimate users. Behavioural baselines help detect:
- Impossible travel and unusual authentication patterns.
- Token abuse and session hijacking.
- Privilege escalation and misuse of privileged accounts.
- Lateral movement between systems.
- Insider-risk indicators.
- Compromised accounts.
Identity threat detection and response (ITDR) focuses on these identity-layer attacks. Its value increases when identity events are correlated with endpoint, network, cloud and application telemetry rather than reviewed in isolation.
3. AI-assisted investigation and natural-language querying
Analysts can increasingly ask questions such as “show failed logins followed by a successful login for this user in the last 24 hours” and receive results without writing a full query. Related capabilities include automated evidence collection, timeline reconstruction, incident summaries, root-cause hypotheses and analyst copilots that follow investigation playbooks.
There is a limit. Natural-language querying does not remove the need for query-language skills. Complex investigations still call for structured queries, custom detections and forensic validation. Analysts should verify what the generated query actually searched.
4. AI-driven detection engineering
Detection engineering is the discipline of designing, testing and maintaining detection rules. AI can support it through:
- Rule recommendations and draft detections.
- False-positive tuning suggestions.
- Threat-hunting support.
- Detection coverage mapping against the MITRE ATT&CK framework, a public knowledge base of adversary tactics and techniques.
- Detection-as-code, where rules are version-controlled, tested and deployed like software.
- Custom detections for cloud and identity threats.
AI can speed this work up, but human validation remains essential. Unreviewed rules can be weak, noisy or blind to the very behaviour they were meant to catch.
5. Automated response and SOAR integration
SOAR stands for Security Orchestration, Automation and Response. A SOAR capability runs playbooks, which are predefined workflows that guide automated or semi-automated actions. AI-powered SIEM increasingly feeds these playbooks with better-prioritised incidents and response recommendations.
Common automated actions include endpoint isolation, account suspension, token revocation, firewall or network policy changes, ticket creation, case management and post-incident reporting.
High-impact actions need care. A wrongly isolated production server or a suspended executive account has a real business cost. The safer approach is human-in-the-loop response: AI recommends or initiates, and a person approves critical actions. Use risk-based approval tiers. Low-risk steps such as enrichment can run automatically; high-impact containment should require sign-off.
6. Cloud-native SIEM and multi-cloud visibility
Cloud-native SIEM architectures offer elastic ingestion, scalable storage and serverless analytics. They suit the telemetry that modern environments produce: cloud workload logs, SaaS application logs, Kubernetes and container events, and API activity across multiple clouds. Data-lake designs also allow cost-efficient long-term retention.
Scalability does not remove the need for discipline. Organisations must still decide what to ingest, how long to retain it, and what data-transfer charges apply between platforms and regions.
7. Unified security data platforms
SIEM, SOAR, extended detection and response (XDR) and threat intelligence are converging into broader security analytics platforms, often built on a security data lake and open telemetry standards. Benefits include cross-domain correlation, fewer data silos and better investigation context.
Convergence also brings trade-offs: integration effort, governance of shared data and the risk of vendor dependency. Check data portability and export options early.
8. Agentic AI in security operations
Agentic AI refers to systems that plan and carry out multi-step tasks using tools. In a SOC, that may mean an agent that gathers enrichment, queries several data sources, drafts an incident assessment and proposes a response.
This is promising but still maturing. It needs strong guardrails: least-privilege permissions, full audit logging, validation of outputs, clear escalation paths and human accountability for decisions. Agentic AI should be treated as an assistant to SOC analysts, not as a substitute for them.
9. Explainable AI and trust
Analysts will not rely on a recommendation they cannot interrogate. Explainability means a system can show:
- Why an alert was generated.
- Which signals influenced a risk score.
- What data was used.
- What actions are recommended.
- Whether the model is behaving as expected.
Analysts must also be able to challenge or override a decision. Explainability supports auditability and prevents teams from blindly following automated output.
10. AI governance and model security
AI used for security is itself something to secure. Key concerns include:
- Access controls over models, prompts and outputs.
- Prompt injection, where malicious text in logs or emails manipulates an LLM’s behaviour.
- Data leakage and handling of sensitive data in prompts and training sets.
- Bias, false positives and false negatives.
- Audit trails and human accountability for AI-assisted decisions.
- Regulatory and privacy obligations, including applicable Indian data-protection requirements.
- Continuous model evaluation to catch model drift, where performance degrades as behaviour and environments change.
Monitor, test and govern AI systems as you would any critical security infrastructure.
AI-powered SIEM architecture
A typical AI-powered SIEM follows this flow:
Telemetry sources → Ingestion and normalisation → AI and analytics → Detection and prioritisation → Investigation and response → Reporting and improvement
|
Layer |
What happens |
|
Telemetry sources |
Endpoints, identity providers, cloud platforms, firewalls, applications, databases, network devices and SaaS tools produce logs. |
|
Ingestion and normalisation |
Data is collected, parsed, enriched and standardised. |
|
AI and analytics |
Behavioural modelling, anomaly detection, correlation, risk scoring and generative-AI assistance. |
|
Detection and prioritisation |
Threats are identified and incidents are ranked. |
|
Investigation and response |
Analyst review, automated playbooks, containment and remediation. |
|
Reporting and improvement |
Compliance reporting, metrics, detection tuning and model evaluation. |
The first two layers decide the quality of everything after them. Poor data gives poor analytics, whatever the model.
Key AI techniques in SIEM
|
Technique |
Role in SIEM |
|
Supervised machine learning |
Learns from labelled examples to classify known patterns. |
|
Unsupervised machine learning |
Finds unusual patterns without labelled data. |
|
Behavioural analytics |
Builds baselines and detects deviations. |
|
Graph analytics |
Maps relationships among users, devices, IPs, applications and events. |
|
Natural language processing |
Powers search, summarisation and incident explanation. |
|
Large language models |
Assist investigation and report generation. |
|
Reinforcement learning |
May help optimise response in controlled settings; needs careful validation. |
|
Generative AI |
Produces summaries, hypotheses and analyst-facing explanations. |
No single technique solves every problem. Effective SIEM needs layered analytics, quality data and human oversight.
Metrics to measure AI-powered SIEM success
Measure operational outcomes, not the number of alerts processed. Capture baselines before enabling AI so that any improvement is real.
|
Metric |
What it measures |
Why it matters |
|
Mean time to detect |
Time from malicious activity to detection |
Shows whether detection is getting faster |
|
Mean time to triage |
Time from alert to initial assessment |
Shows queue efficiency |
|
Mean time to investigate |
Time spent understanding scope and cause |
Shows analyst productivity |
|
Mean time to respond |
Time from confirmation to action |
Shows response readiness |
|
Mean time to contain |
Time to stop spread |
Directly limits impact |
|
False-positive rate |
Share of alerts that are not real threats |
Indicates noise and wasted effort |
|
Alert-to-incident ratio |
Alerts needed to produce one real incident |
Shows alert quality |
|
Analyst workload per incident |
Effort hours per case |
Reveals real capacity gains |
|
Detection coverage |
Share of relevant ATT&CK techniques with tested detections |
Exposes blind spots |
|
Automation success rate |
Share of automated actions that complete correctly |
Tests reliability of playbooks |
|
Escalation rate |
Share of incidents escalated to senior staff |
Shows triage accuracy |
|
Cost per investigated incident |
Total cost divided by incidents handled |
Links security to finance |
|
Analyst satisfaction |
Team feedback on tools and workload |
Early signal of burnout and trust |
|
Business disruption from automated response |
Outages or user impact caused by automation |
Keeps automation safe |
Implementation challenges
Adoption is not automatic. Common obstacles include:
- Poor-quality or incomplete telemetry, and inconsistent logging.
- Excessive ingestion costs.
- Weak identity and asset context.
- Siloed tools and integration complexity.
- Insufficient detection engineering and a skills shortage.
- Persistent alert fatigue.
- Lack of trust in AI recommendations, or the opposite problem, over-automation.
- Privacy and compliance risk.
- Model drift.
- Unclear ownership between security, IT and data teams.
Begin with a few high-value use cases, establish baselines, and expand automation gradually.
Best practices for adopting AI-powered SIEM
- Start with a clear use case, such as identity threats, cloud threats, phishing or alert triage.
- Set data-quality standards before enabling AI.
- Define asset criticality and business context.
- Prioritise by risk, not by severity labels alone.
- Keep humans in the loop for high-impact response.
- Build explainability into alerts and investigations.
- Tune detections and models continuously.
- Use threat intelligence and MITRE ATT&CK mapping.
- Establish AI governance and audit trails.
- Measure outcomes against defined SOC KPIs.
- Train analysts to work with AI-assisted tools.
- Test before enabling autonomous response, with approval workflows.
- Review AI decisions regularly, including missed detections.
- Balance automation with operational resilience, with manual fallbacks.
Strengthen Security Operations with Cyfuture Cloud
AI-driven security operations rest on infrastructure that is secure, scalable and well monitored. Cyfuture Cloud can support organisations modernising their SOC as an infrastructure and cloud partner, through:
- Secure cloud infrastructure for hosting security analytics and data platforms.
- Scalable compute for log processing, analytics and AI workloads.
- Cloud-native workload visibility and monitoring and observability for telemetry sources.
- Data protection and access controls, including encryption and role-based access.
- Network security to segment and protect security tooling.
- Identity and access management to enforce least privilege.
- Compliance-ready infrastructure to support audit and retention needs.
- Support for AI and security workloads, including GPU-backed compute where applicable.
Future outlook
AI-powered SIEM is likely to keep moving towards more contextual detection, deeper automation, a better analyst experience, wider cloud and identity coverage, stronger governance and more integrated security data platforms. AI agents will probably take on more routine investigation, within controlled limits of autonomy.
Conclusion
AI-powered SIEM will not replace security teams, but it will change how they work. It can improve speed, context, prioritisation and analyst productivity, provided the data is sound, the detections are well engineered and the decisions are explainable and governed. The most effective SOCs in 2026 will pair AI capabilities with skilled analysts, strong data foundations, disciplined detection engineering and clear accountability.

Stay Ahead of the Curve.
Join the Cloud Movement, today!
Send this to a friend